Bug Inspect checks a customer's bug report against your code before it reaches your team. When a report looks like a real defect, an engineering agent reproduces it in a sandboxed copy of your repository, writes a fix, and opens a draft pull request for a teammate to review.
Bug Inspect needs a linked GitHub repository and a paid plan or an active trial.
Where to find it
Settings → AI → Bug Inspect, at /settings/ai/bug-inspect.
Turn it on
Link a GitHub repository under `Settings → Integrations → GitHub`, if you haven't already.
Turn on `Check bug reports against the code` on the Bug Inspect page.
Once Bug Inspect is live for your workspace, a `Write access` row appears below it. Click `Install App` so Bug Inspect can open pull requests, a separate GitHub App from the one that reads your repository for the help center.
If a GitHub Actions workflow in your repository can read a secret, review it under `Workflow secrets` and click `Acknowledge`.
Runs stay paused while a workflow could hand a secret to Bug Inspect's test code, until an admin reviews and acknowledges it. Editing that workflow again asks for review a second time.
How it works
A customer describes a bug to the Productlane Agent in the widget. Once the agent has already filed a Linear issue for it, it hands the report to Bug Inspect.
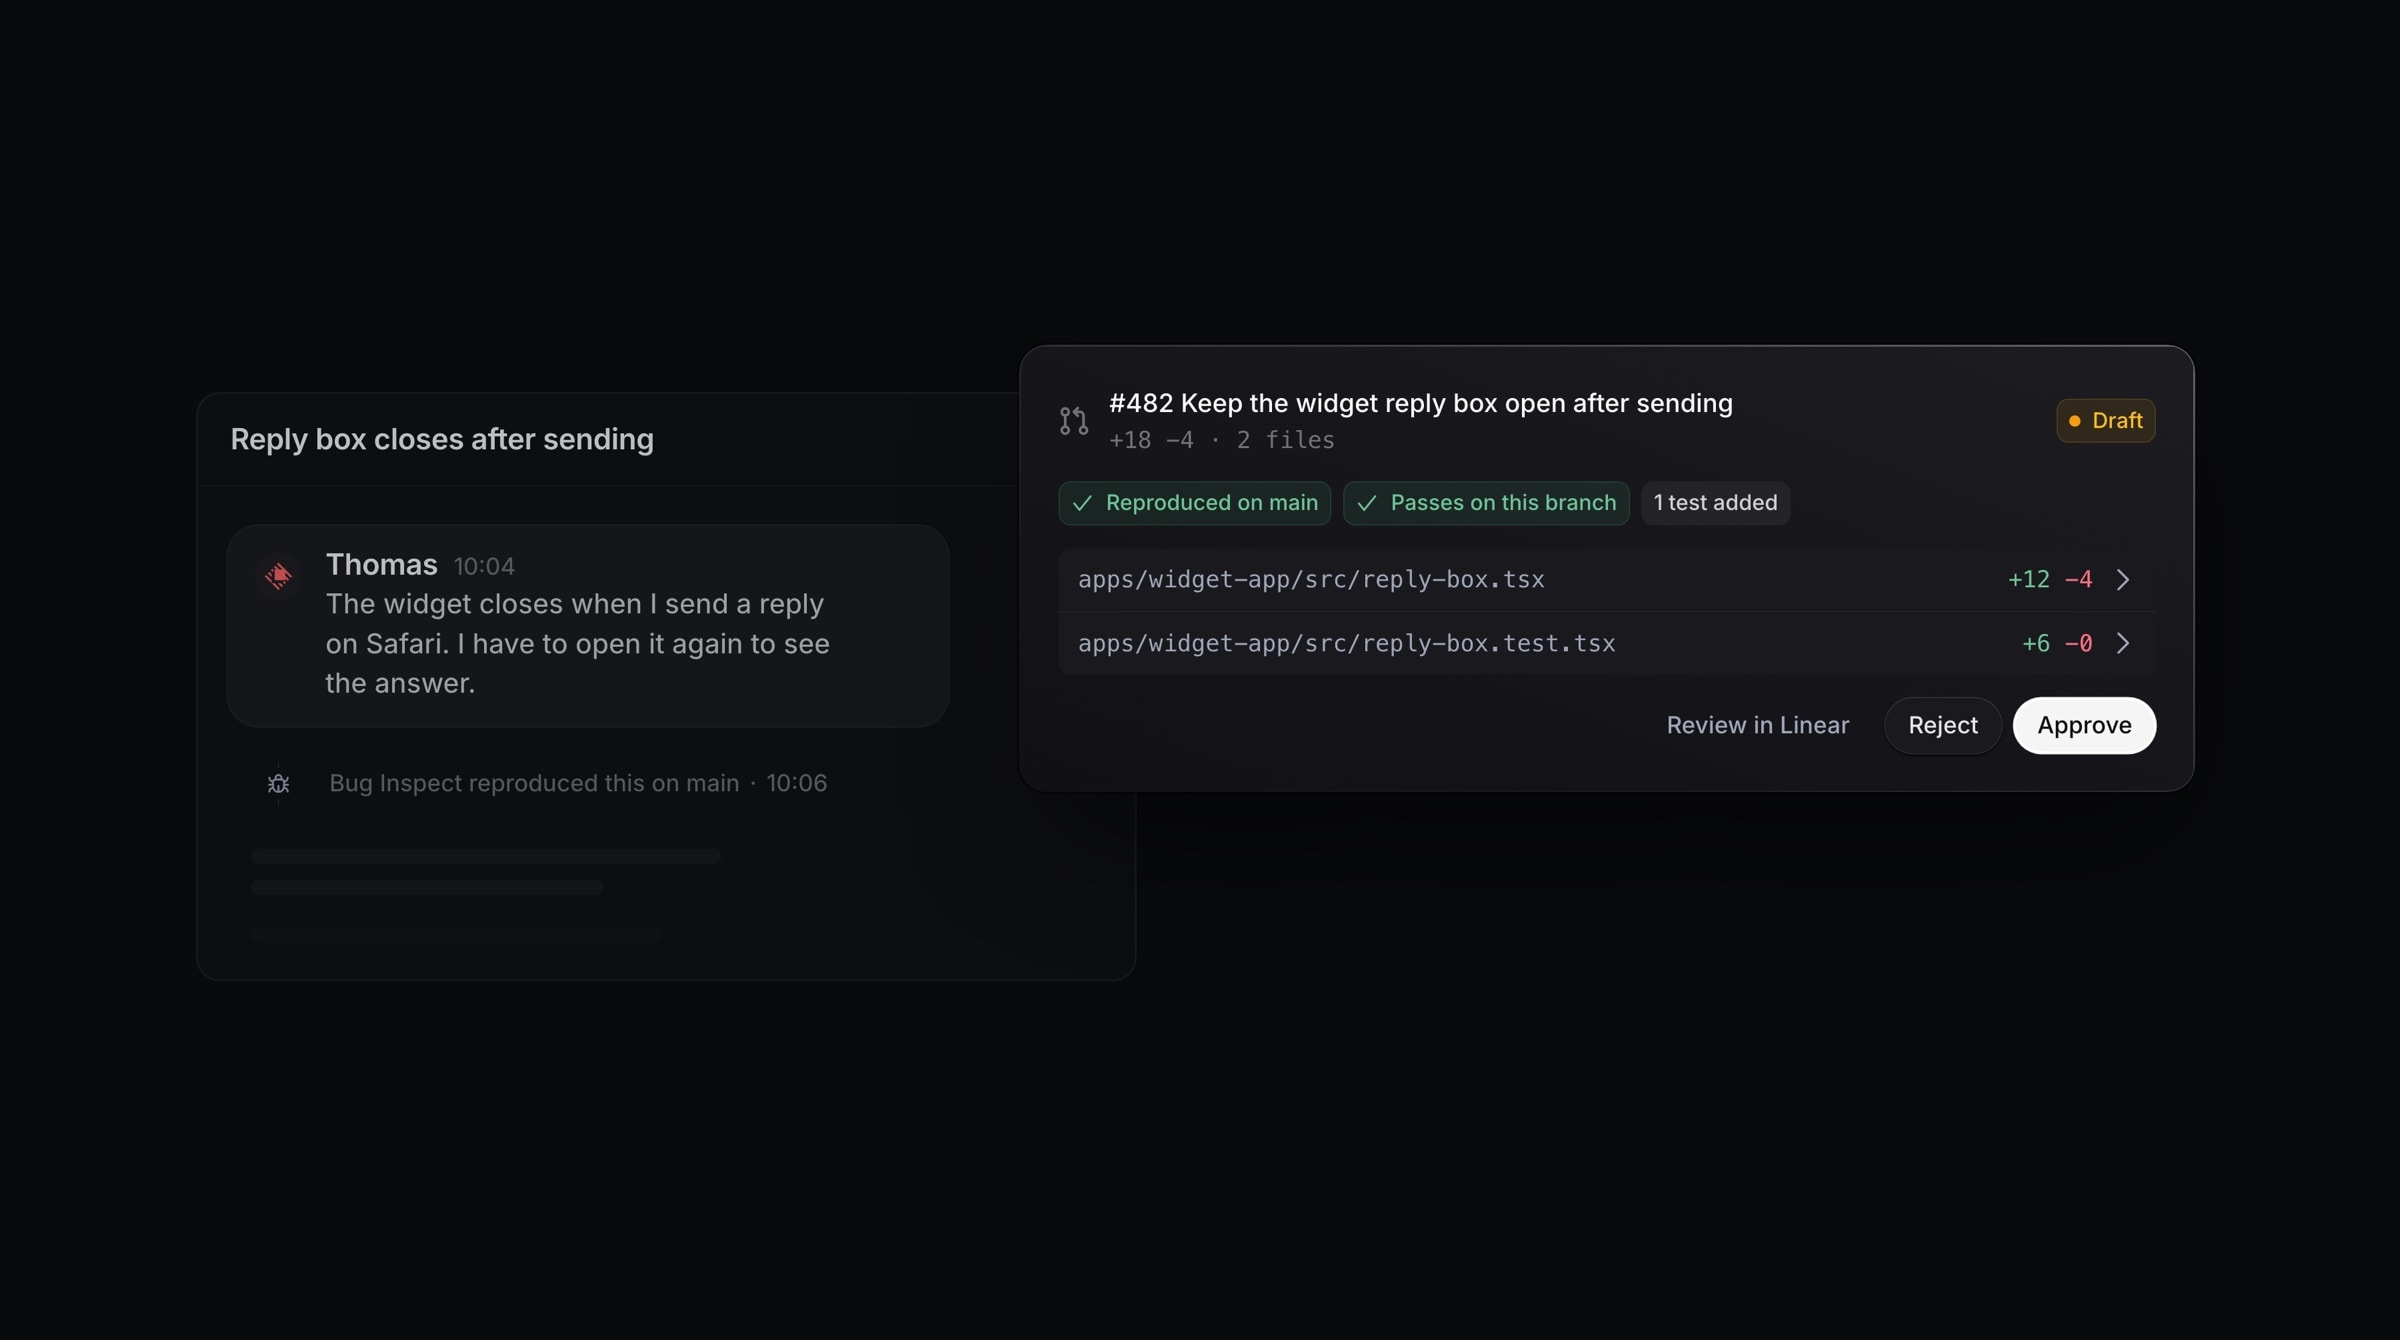
Bug Inspect reproduces the bug in a sandbox: it writes a test that fails for the reason the customer described, then writes the smallest fix that makes it pass.
When it reproduces and fixes the bug, it opens a draft pull request and posts a review card on the thread's timeline. The card shows the diff with one tab per file and a
Full viewbutton, plus a "Reproduced on" badge naming the branch.A teammate reviews the diff from the thread. The card's merge box shows the pull request's current state in GitHub. Pick squash, merge, or rebase from the merge button, using whichever methods your repository allows. Click
Update branchwhen the branch has fallen behind, or clickClose pull requestto close it.When Bug Inspect can't reproduce the bug, it asks the customer for more detail or escalates the report to your team, depending on what was missing. A run that breaks for another reason, such as a sandbox timeout, escalates too instead of closing the report quietly.
Merging or closing the pull request sends the customer no message.
Good to know
Bug Inspect only reads your repository. The sandbox can reach your package registry to install existing dependencies and nothing else, and no file name or line of code reaches the customer, whatever the outcome.
A customer's message is read only as a bug description. Text in a report that tries to redirect the agent or name files to change doesn't change what Bug Inspect does.
A fix can't touch CI config, Dockerfiles, lockfiles, or anything under
.github/or.claude/, and it tops out at 10 files or 300 changed lines.Only a Member or Admin can merge or close the pull request. A Viewer sees the review card and the pull request's state but can't act on it.
Bug Inspect only triggers from a verified contact's conversation with the Productlane Agent in the widget, not from email, Slack, Microsoft Teams, or an anonymous visitor.
When a run is blocked, the
Did not runnote on the run and the thread timeline both give the reason. One example is the workspace reaching its limit of 10 pull requests for the day.Write accessandWorkflow secretsappear once Bug Inspect is live for your workspace. Until then, the toggle alone has nothing more to configure.